Click, Ship and Pass the Audit
Drag, drop, and instantly lock your software artifacts with post-quantum security and automated compliance. No cloud, no keys to manage, no friction.
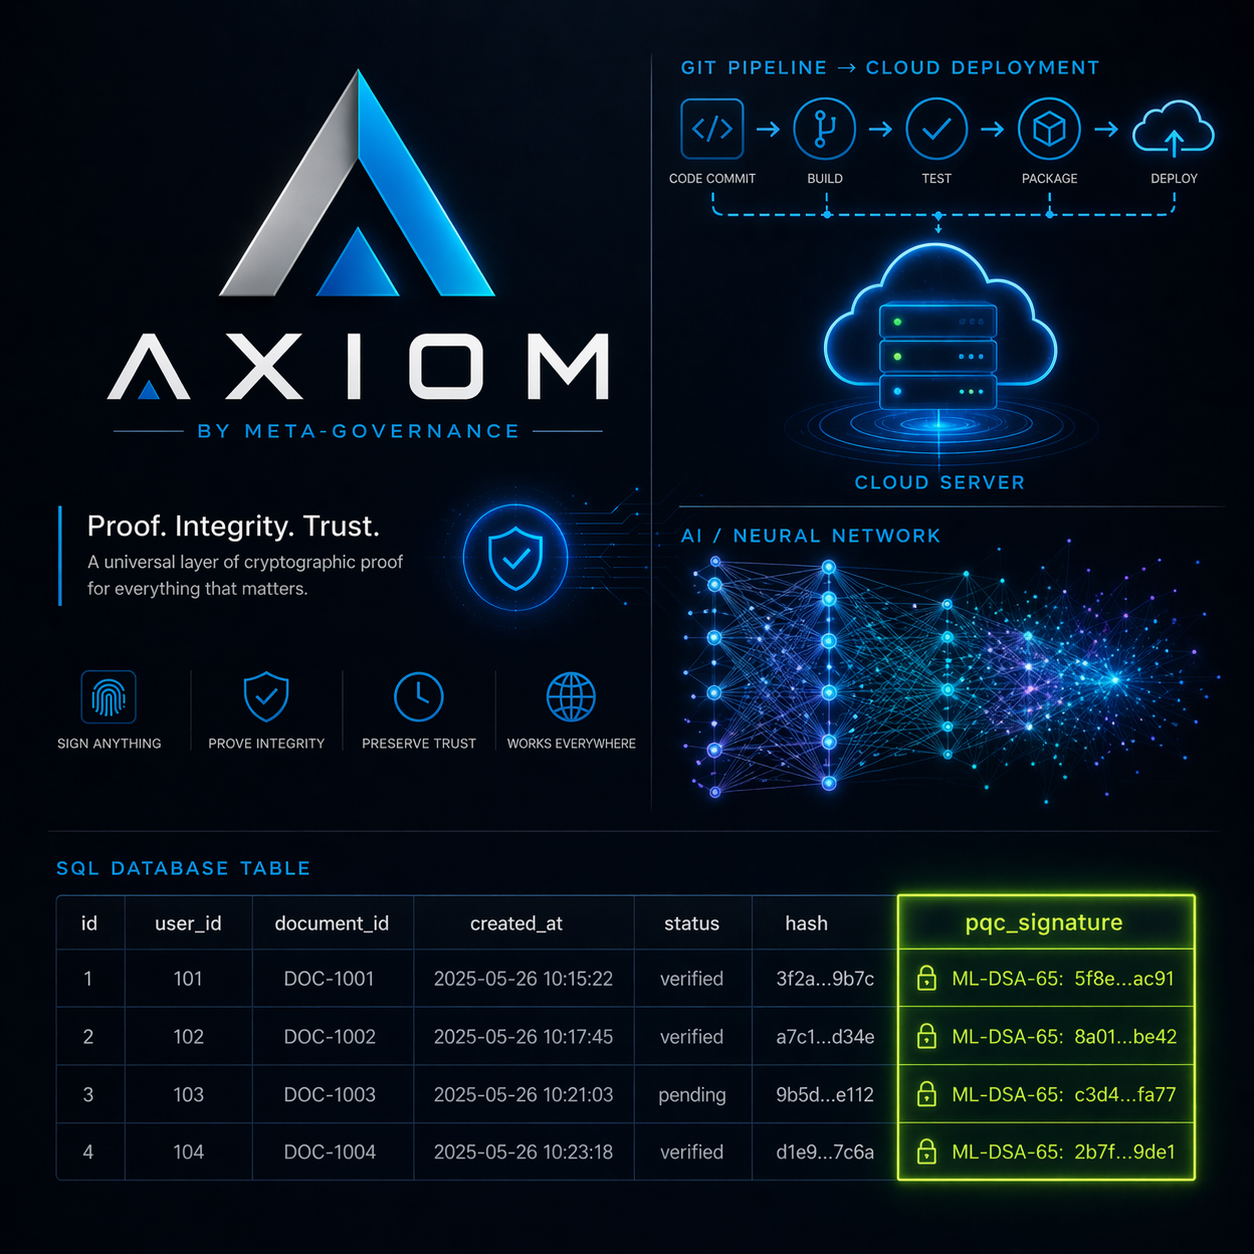
See Axiom in Action
Watch how Axiom secures software artifacts and automates compliance in real time.
Compliance in Three Clicks
Instantly anchor, attest, and secure your supply chain without the overhead of cloud certificate systems.
1. Drag & Drop
Select any binary, library, or whole directory directly inside your local dashboard.
2. One-Click Seal
Axiom indexes dependencies, compiles the report, and locks it with post-quantum math.
3. Deliver with Confidence
Distribute a secure, self-contained bundle that customers verify instantly on their end.
payload.exe
Ready to Seal (SHA-256: d8f1...392a)
release.axiom.zip
Validated Attestation & Provenance Package
Axiom Signer Console
Simulate a local post-quantum signing execution. Choose your hardware/software key anchor model, supply a payload, and generate an attested ML-DSA-65 signature.
Signer Configuration
Axiom Capsule
Self-verifying digital asset distribution for the post-quantum era.
Axiom Capsule packages files and folders together with cryptographically signed evidence, allowing recipients to independently verify authenticity before extracting the payload. Every Capsule carries its own cryptographic proof, enabling portable, offline verification without relying on external verification infrastructure.
Built-In Verification
Explore the design characteristics that make Axiom Capsule a resilient distribution vector.
Self-Verifying Distribution
Recipients verify authenticity, provenance, and structure before payload extraction, preventing premature code execution.
Embedded Evidence
Carries signed provenance, integrity manifests, CycloneDX SBOMs, and software supply chain evidence in a single file.
Offline Verification
Verification requires zero network calls, cloud lookups, or third-party APIs. Runs locally on air-gapped systems.
Cross-Platform Delivery
Capsules can be created on one operating system and distributed to another while preserving original cryptographic signatures.
Post-Quantum Protected
Built directly on the Axiom post-quantum verification engine using FIPS 204 ML-DSA-65 algorithms.
Local First
Packaging and verification processes execute entirely on the host machine, keeping private details safe inside your network.
Delivery Workflow
A step-by-step cycle demonstrating secure packaging, transport, and trusted extraction.
Select Payload
Select files or folder to package
Generate Capsule
Append package and binary footer
Distribute Anywhere
Deploy portable executable file
Recipient Verifies
Inspect and run offline checks
Payload Extraction
Extract trusted digital assets
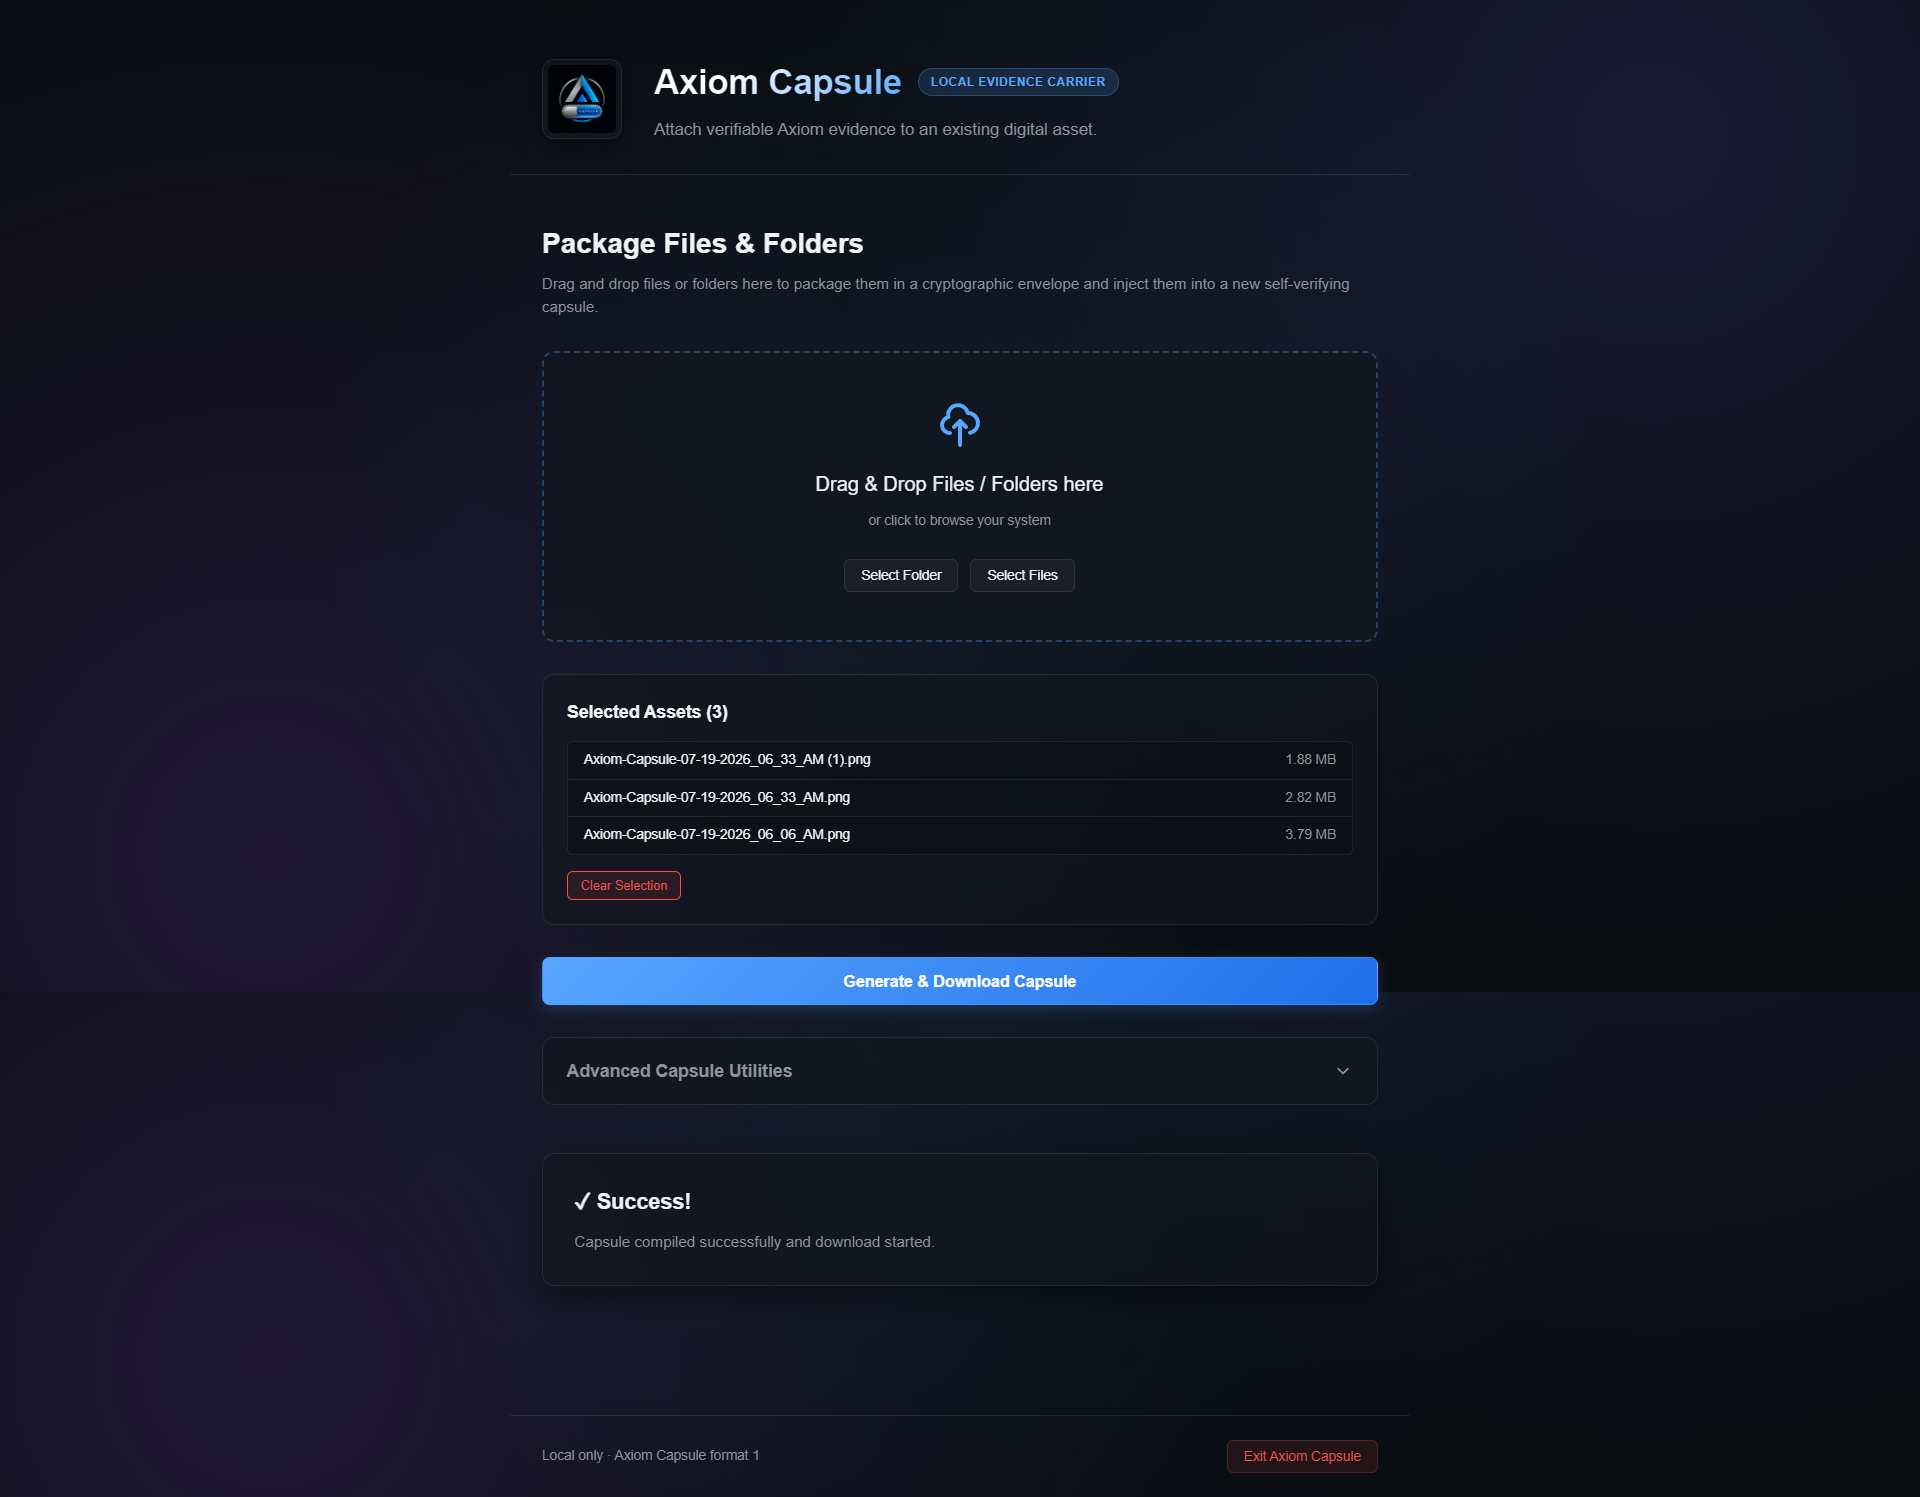
Axiom Capsule Interface
Review the visual workflow templates for capsule creators and validation recipients.
Create Capsule
The Capsule Builder integrates directly into local environments to bundle artifacts securely into executable shells.
- Drag and drop files or folders
- Generate a Capsule
- Embed cryptographically signed evidence
- Produce a self-verifying digital asset
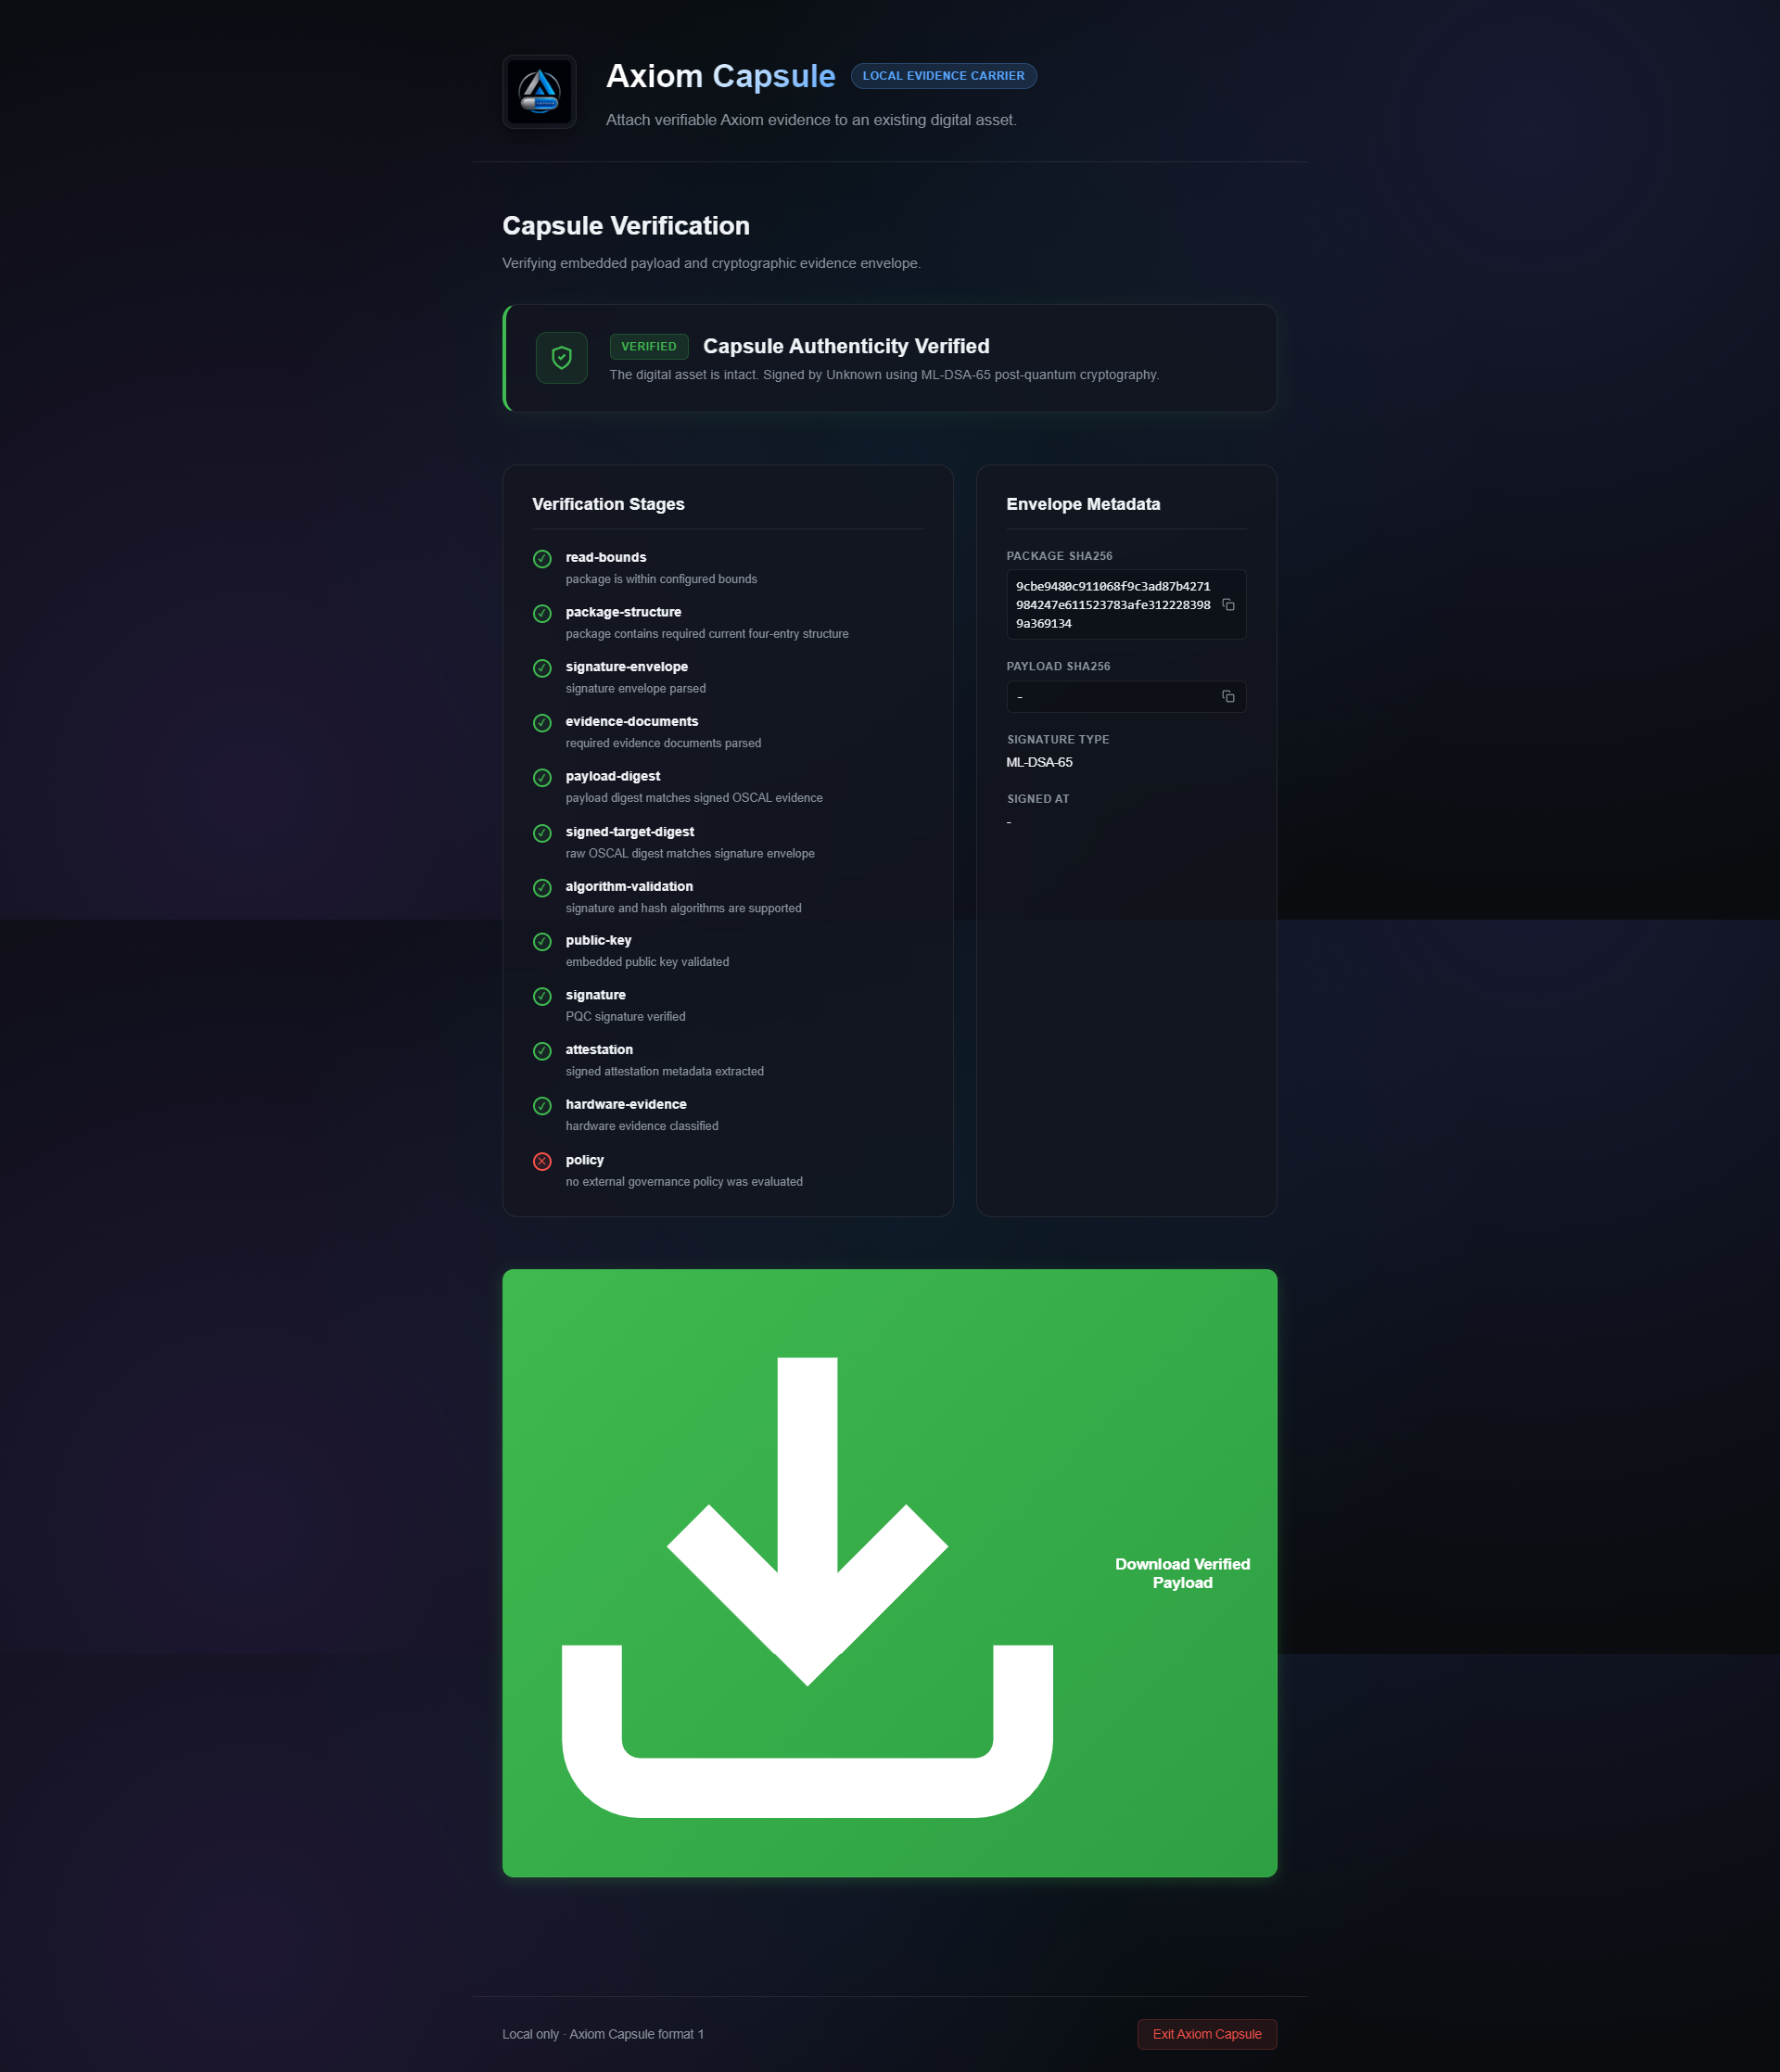
Verify Capsule
The embedded verifier guarantees that the payload remains untampered before allowing extraction.
- Verify Capsule Integrity and footer offsets
- Layered Verification Stages
- View Embedded Evidence
- Inspect Hardware Claim certificate status
- Download and extract verified payload safely
Product Ecosystem
Axiom Capsule functions as the delivery component of the broader Axiom post-quantum platform.
| Product | Purpose |
|---|---|
| Axiom Signer | Creates cryptographic identity |
| Axiom Identifier | Packages signed evidence |
| Axiom Capsule | Delivers trusted digital assets |
| Axiom Verify | Independently validates authenticity |
How Axiom Operates
A stateless signing pipeline that eliminates cloud keys, external API dependencies, and security perimeter leaks.
Tamper-Proof Proof of Origin
Anchoring software to local hardware ensures customers always know exactly where a delivery came from.
- Verified locally against manufacturer roots
- Local factory certificate check blocks emulated/virtualized TPMs
- No external HTTP/lookup dependencies
Zero Key Management
Because the hardware is the identity, there are no private key files to lose, copy, or leak.
- Private signing parameters never leave TPM
- Zero filesystem trace of private credentials
- Identity is bound to physical motherboard
Future-Proof Compliance
FIPS 204 ML-DSA serves as the immediate answer to meeting federal supply chain mandates alongside automated SBOM delivery.
- Maintains 100% JSON readability for seamless GitOps diffs (no opaque JWS/DSSE wrapping)
- Air-gapped compatible envelope output
- Easily matches existing DevOps pipelines
A New Trust Architecture
Traditional systems protect secrets. Axiom protects identity.
| Feature / Vector | Traditional Cloud / Key Vaults | The Axiom Architecture |
|---|---|---|
| Where is your security stored? | Scattered software key stores, files, or cloud vault APIs. Copyable by admins or attackers. | Un-copyable, physical silicon hardware blocks (motherboard TPM 2.0). |
| Does it need an internet connection? | Requires active cloud connection, key retrieval tokens, or external API endpoints. | 100% air-gapped, offline execution. Zero network calls required. |
| How is it delivered? | Loose, easily modified JSON files that are decoupled from the binary. | A single, self-contained secure .axiom.zip bundle. |
Download Axiom Identifier & Documentation
Get the local desktop app to orchestrate supply chain compliance or review the technical documentation.
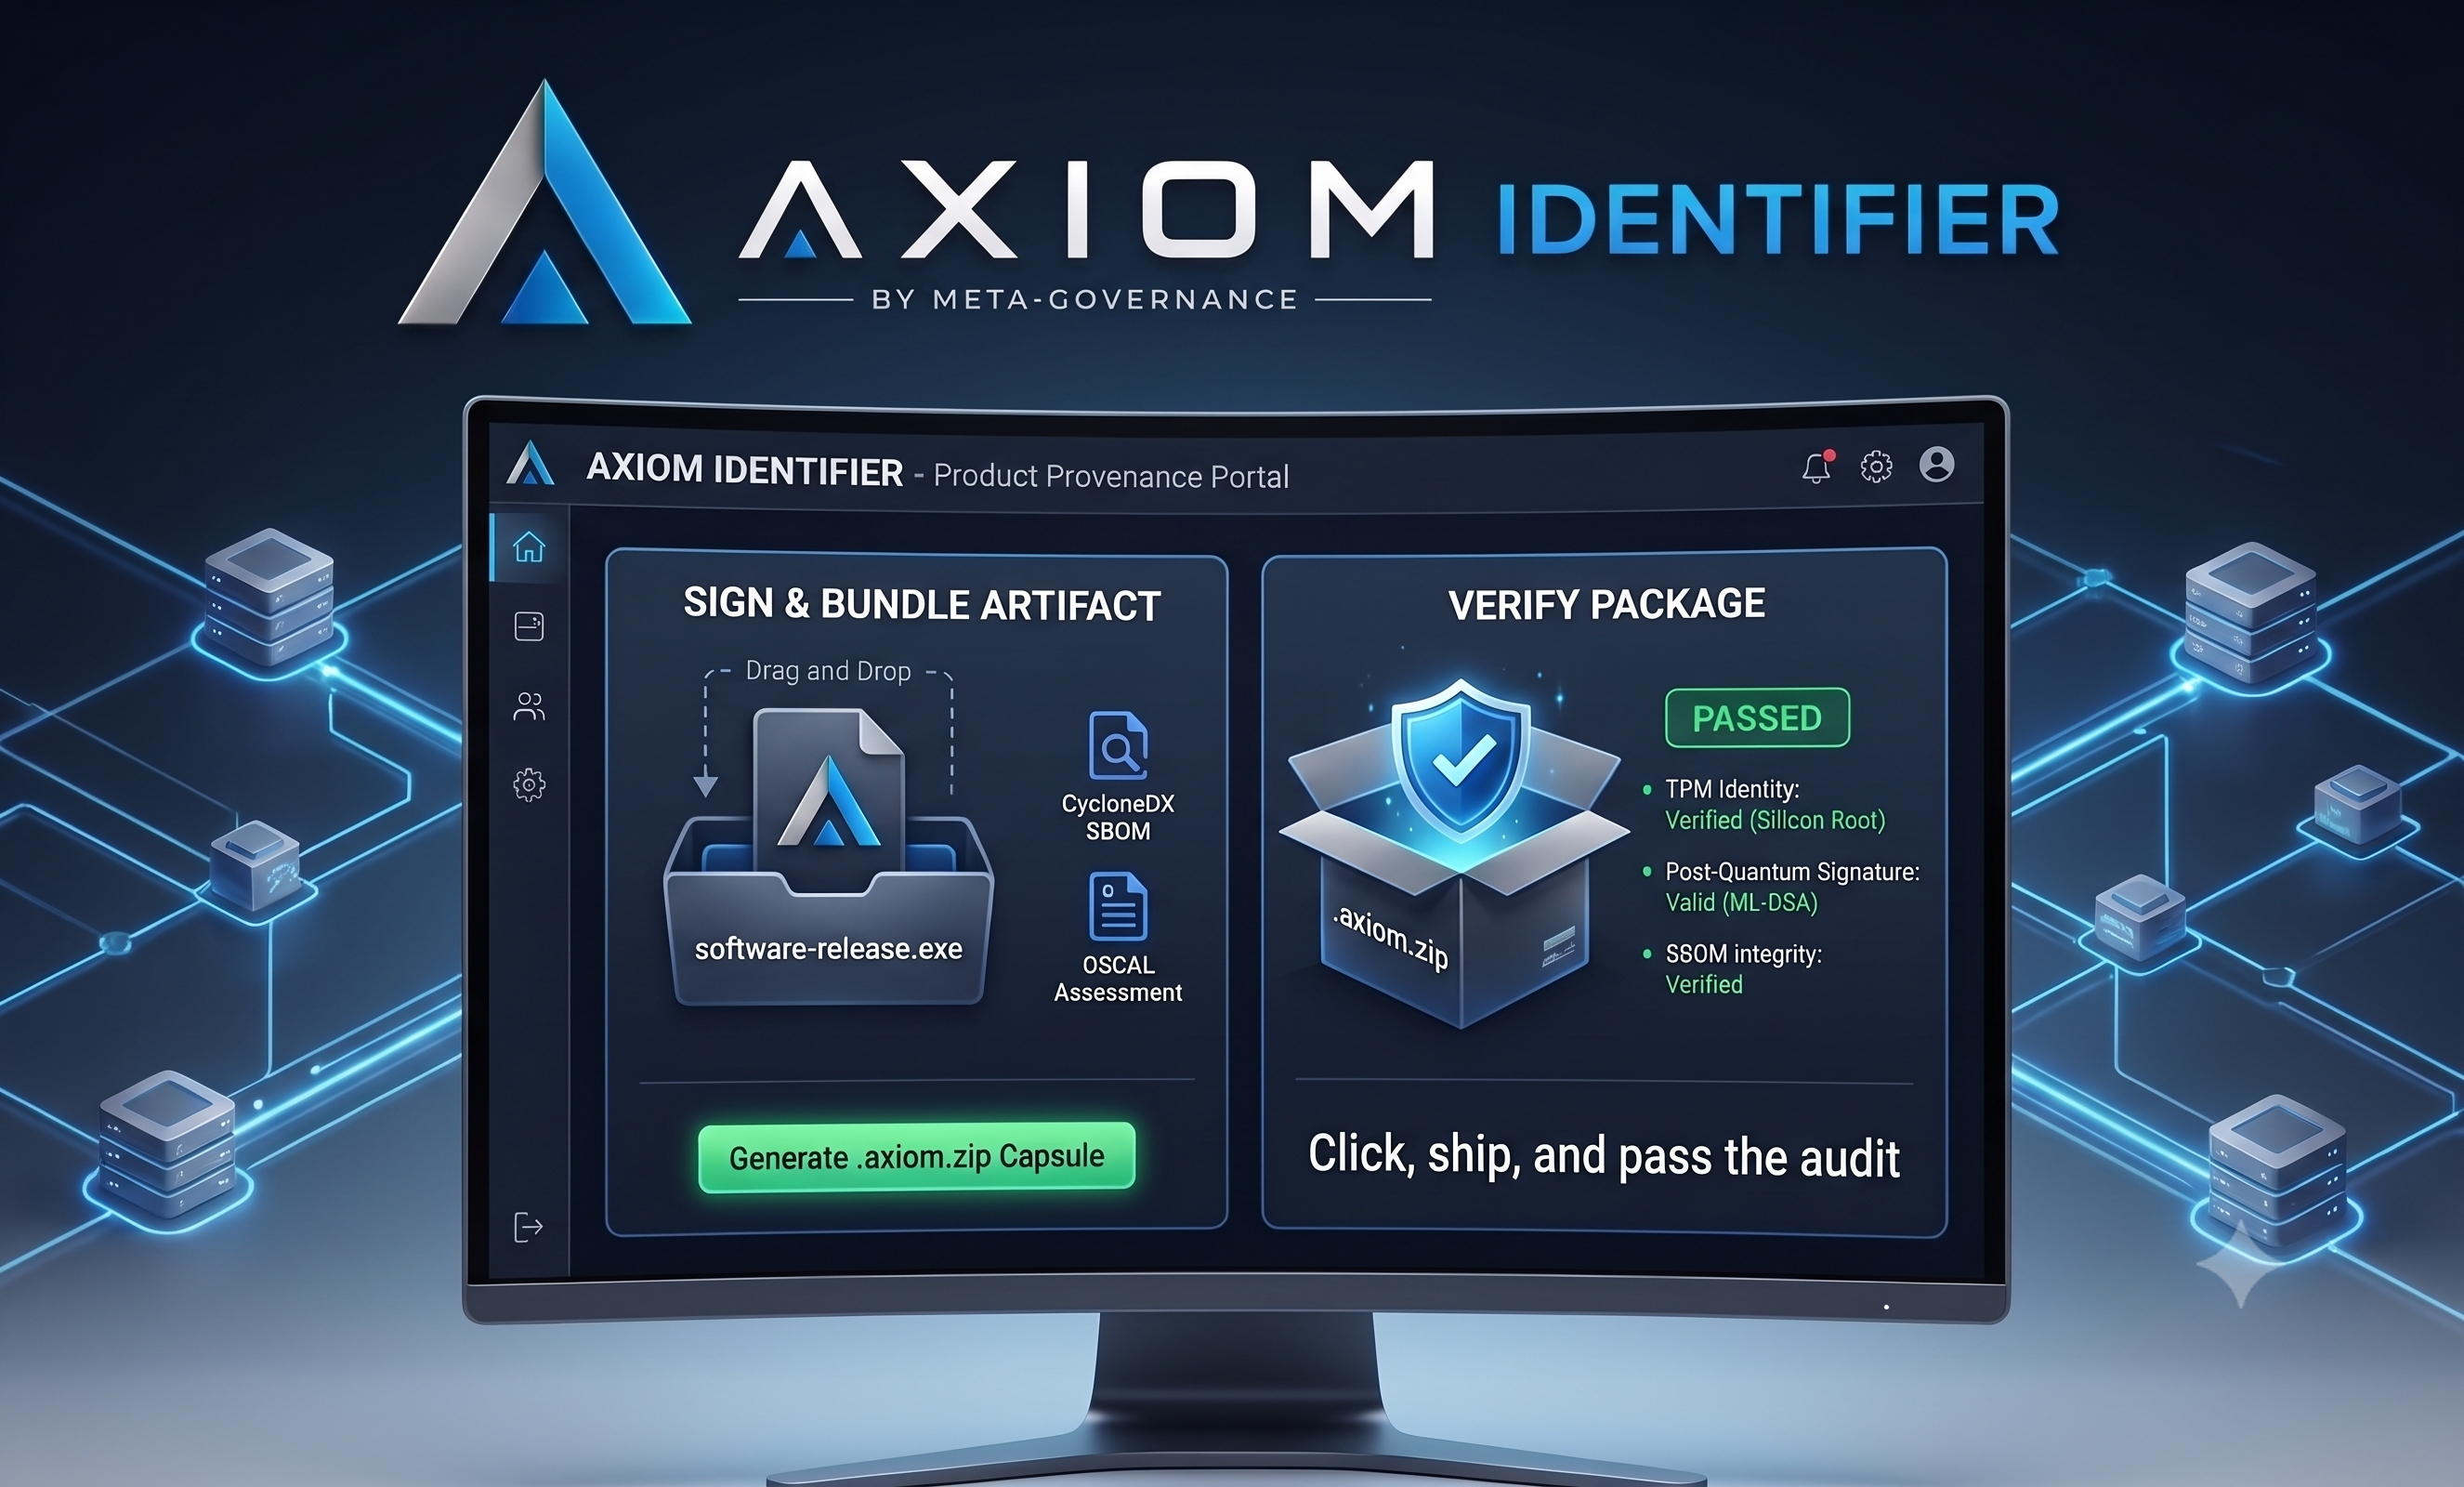
Axiom Identifier App
Local-first desktop utility to package payloads, execute TPM hardware signing via TBS, and generate automated CycloneDX and OSCAL compliance envelopes.
Technical White Paper
Detailed architecture documentation on local TPM certification, FIPS 204 implementations, and DevSecOps integrations.